MCP & Agent Skill Trust Brief
MCP & Agent Skill Trust Brief
Know what a tool does before you install it
Review an MCP server, AI agent skill, or coding-agent plugin before giving it access to your files, services, or credentials.
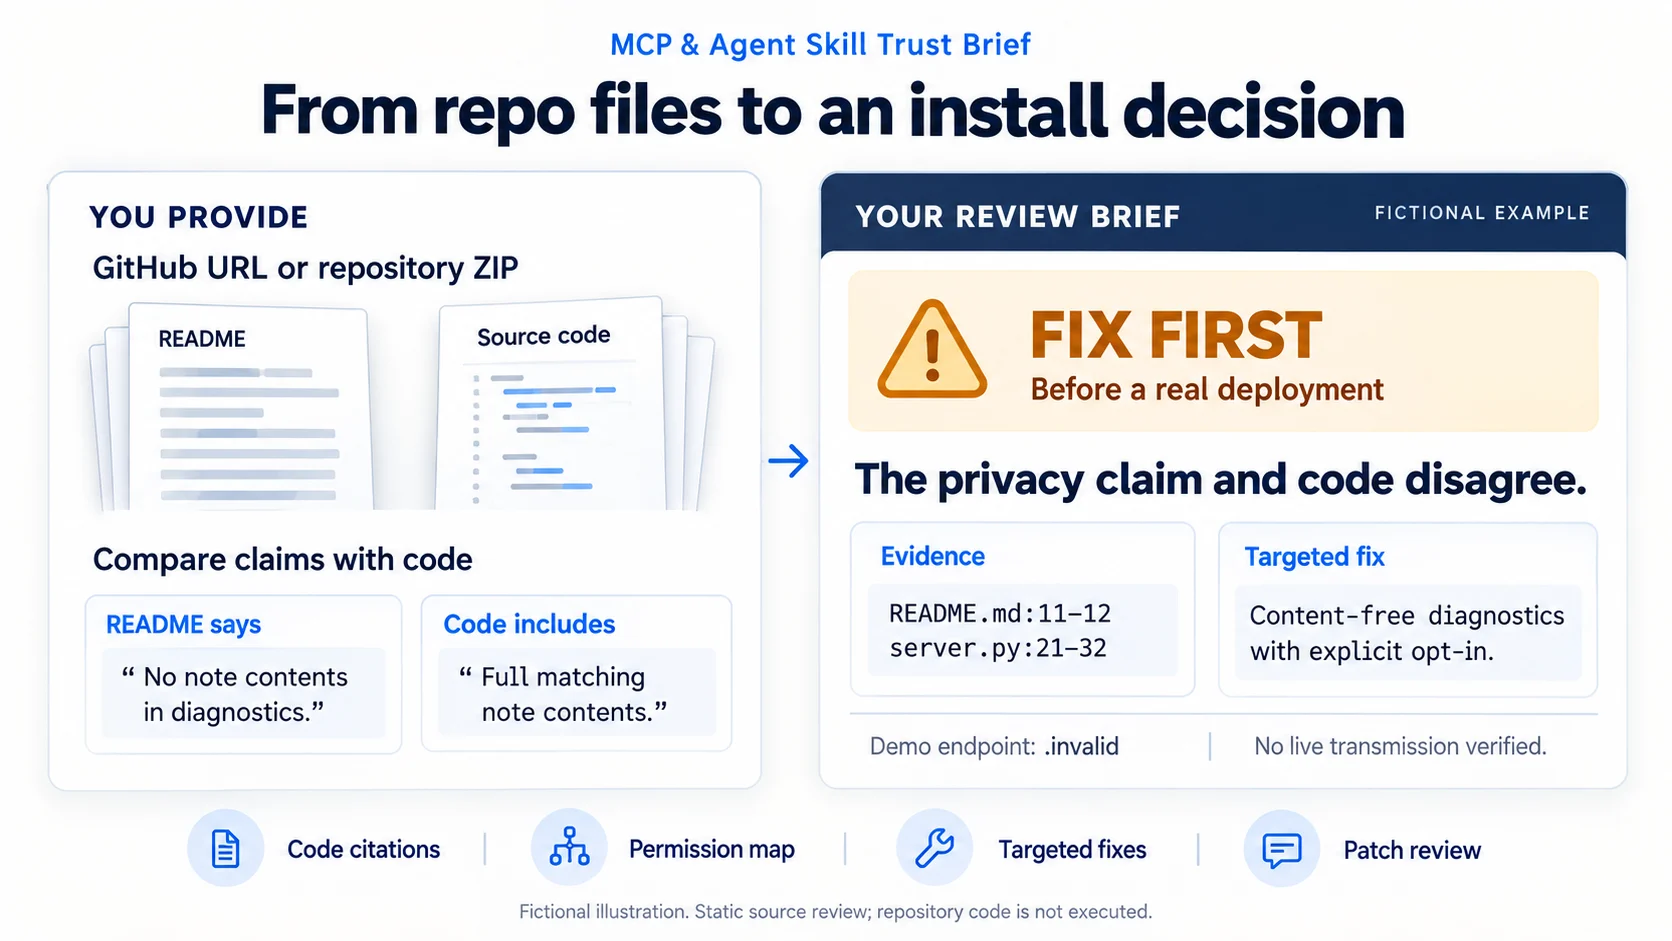
Share a GitHub URL or upload repository files. Get a clear install decision, the evidence behind it, and practical changes to address important concerns.
What you get
- Install decision: Reasonable to install, Caution, Fix first, or Do not install—with the reviewed scope clearly stated.
- Permission and data-flow map: What the tool reads, writes, runs, and sends; where data goes; and what triggers the behavior.
- Documentation checks: Important differences between README promises, tool descriptions, and actual code.
- Evidence-backed findings: File references and line numbers when available, with severity and confidence assessed separately.
- Targeted fixes: The smallest useful changes to address the main concern.
- Patch review: Send a revised version to check what was resolved, what remains open, and whether new concerns appeared.
Judgment beyond a checklist
Broad file access may be expected for a filesystem tool. Missing tests or a lockfile do not, by themselves, prove harmful behavior.
The review focuses on whether capabilities fit the tool’s purpose, whether sensitive actions are disclosed, and what the supplied evidence actually establishes.
Start with one question
“Is this MCP server safe to install?”
Attach a repository ZIP or share its GitHub URL. You can also provide README files, SKILL.md, dependency metadata, source snippets, or scanner reports.
If important files are unavailable, the brief identifies the gap and the specific evidence needed.
Review scope
Static source review only. The Agent does not execute repository code or install its dependencies. Findings distinguish source behavior from unverified runtime behavior; the review is not a security certification.