
要件を書いたはずなのに、開発途中でルール不足や仕様の曖昧さが見つかり、手戻りが発生していませんか? Agile ScopeGuard Pro は、PM・Engineering・QA の視点から要件を整理し、Functional Specification、User Story、Acceptance Criteria、QA Test Cases、API、Workflow、リスク、Implementation Checklist まで構造化します。 開発前にスコープ・ルール・検証条件を明確にし、認識ずれと手戻りを減らします。

I specialize in safe Codex skill onboarding. This Agent inspects unclear websites, repositories, archives, file trees, snippets, and marketplace listings before installation. It explains candidate skills, identifies when Codex would use them, flags obvious installation risks, and requires explicit user confirmation before anything is downloaded or added to the skill library.

Defensive application-security auditing: turns a repo, manifest, or code snippet into an actionable report—dependency vulnerabilities, leaked secrets, insecure code patterns, and config hardening—mapped to OWASP Top 10 and ranked by severity. Finds risk and the fix only, never attack content.
Audit AI agents, Skills, MCP configurations, tool permissions, and coding-agent setups for prompt injection, excessive agency, credential exposure, data leakage, unsafe code execution, supply-chain risks, memory risks, missing approval controls, and runaway autonomy. Get a calibrated Security Score, Audit Confidence, evidence-backed findings, remediation steps, verification checks, and residual-risk analysis.
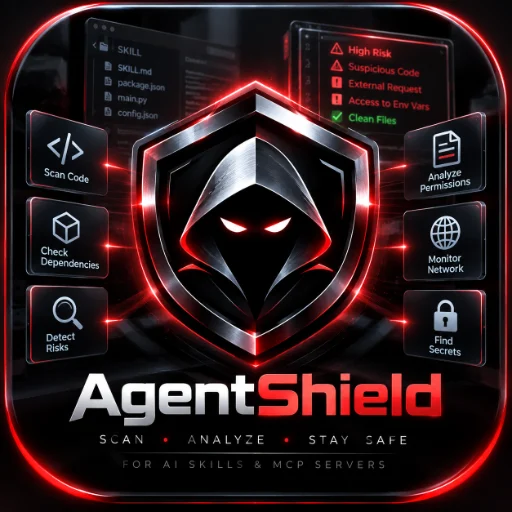
Scan AI Skills and MCP servers before installation. Detect risky scripts, permissions, dependencies, network access, credential exposure, file changes, and suspicious configurations — then generate a clear evidence-based security report.
Paste your Playwright, Puppeteer or Selenium symptom; get ranked causes, probe code and a read-back check.

Your agent reads user-pasted text, web pages, retrieved docs, or tool output — and you can't tell which sentence an attacker wrote. A one-line "ignore malicious instructions" never held. This delivers a layered injection-defense design: threat model, attack-surface map, input/privilege/output defenses, canary tokens and a classifier, an adversarial red-team set with before/after, and residual risk plus an incident runbook.
Audits your test suite's output for silently vanished tests, unexplained skips, and suspiciously fast runs — turns green CI into a real signal.