
Turns a user story or ticket into a verified, minimal test suite. Derives every case from a formal technique (boundary value analysis, equivalence partitioning, decision tables), reduces configuration combinations pairwise, and runs a deterministic script to prove coverage instead of just listing cases. Includes a security pass built from real OWASP findings and Playwright export.

Know if your backtest is a real edge or overfit noise. Runs bar-permutation MCPT, Deflated Sharpe, PBO/CSCV, Hansen SPA, Romano-Wolf StepM, a stationary bootstrap and an out-of-sample split on your own returns — no market feed, no API keys.
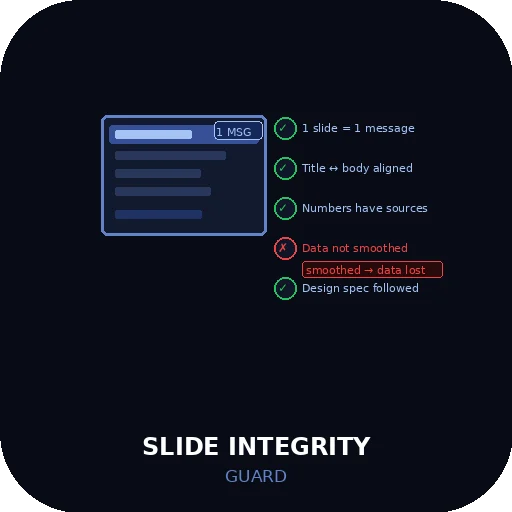
Runs five integrity checks on every slide before output — one message per slide, title-body alignment, number preservation, source citation for every data point, and design spec compliance — blocking any slide where data has been smoothed, sources are missing, or the title contradicts the body.
Verify webhook duplicates, signatures, retries and ordering in isolated local tests. Compare HTTP delivery with business evidence. Includes 18 scenarios, HTML/JSON/JUnit reports and complete English + Traditional Chinese guides.

Audits soccer analysis before conclusions are trusted: source tiers, dates and seasons, competition splits, 450-minute sample checks, availability flags, and uncertainty labels.

Produce structured browser QA evidence for web flows, landing pages, and app screens.
Pre-submission quality gate for AI-generated broadcast scripts. Catches timing errors, sponsor name mistakes, host voice drift, missing stage directions, and unverified facts before they reach production. 8 documented failure patterns. Works for podcasts, YouTube, and live broadcast.

Run authorized penetration tests / vulnerability assessments end to end: Rules of Engagement (authorization & scope) → recon/enumeration → OWASP Top 10 review → CVSS triage → concrete remediation → a formal assessment report for executives and engineers. Defense-focused: it centers authorization management, systematic enumeration, risk evaluation, and a client-actionable deliverable — not offensive payloads. Authorized targets only; no DoS, destruction, or evasion.